- PlatformCore Detection & ResponseEDRAdvanced endpoint detection and response with deep visibility, autonomous containment, and analyst-driven investigationNDRNetwork detection and response powered by full packet capture, session reconstruction, and AI-driven anomaly detection.CloudUnified cloud protection across workloads, identities, and SaaS apps, combining visibility with runtime defense.MobileEndpoint security for iOS and Android, detecting malicious apps, phishing attempts, and device-level exploits.IoT/OTCritical asset visibility and threat detection for industrial and IoT environments—without downtime or blind spots.Human Threat Actor CoverageIntelligenceGlobal threat intelligence aggregated from 300+ sources, mapped to your environment for real-time detection and context.Attack ValidationAutomated adversarial validation to confirm detections, test controls, and prioritize real threats over noise.DeceiveDeception technology that lures attackers into decoy environments, revealing tactics before damage is done.IdentityIdentity threat detection and protection with real-time monitoring of Active Directory, Entra ID, and credentials.Post-Breach Forensics & IRPacketsFull-fidelity network forensics with packet capture, file extraction, and retrospective analysis.SIEMCentralized log management and correlation across all telemetry sources for complete security visibility.ReconContinuous adversarial exposure management—simulating attacker reconnaissance to surface hidden weaknesses.
- MDR
- Why LMNTRIX
- Active Defense
- Use CasesBusiness Use CasesReliable & Thorough CybersecurityElevate Security OperationsCross Product CorrelationTech Use CasesCloud Security SimplifiedOptimizing SIEM Security with Next-Gen Detection ToolsAchieve Excellence in Security OperationsComprehensive MITRE ATT&CK Coverage for All StagesEnvironment Use CasesMDR for AWS Cloud Security – 24/7 Detection & ResponseManaged Detection & Response for Google Cloud SecurityAdvanced Microsoft MDR Security for Threat Defense
- LMNTRIX vs the CompetitionLMNTRIX vs other vendorsvs. CrowdStrikeOverhyped, Overpriced & Always Breachedvs. SentinelOneLimited protection, unable to prevent breachesvs. MicrosoftComplex operations increase TCOvs. Palo Alto NetworksDifficult to implement, operate, & maintainvs. SophosOverpriced and Overcomplicatedvs. Trend MicroLimited to own ecosystem & threat of DevOps interruptionsvs. DarktraceOver-promises with flashy AI marketing but always under-deliversvs. other MDRsSlow MDRs that miss threats and leave you to fix the damage
- Ask LISA
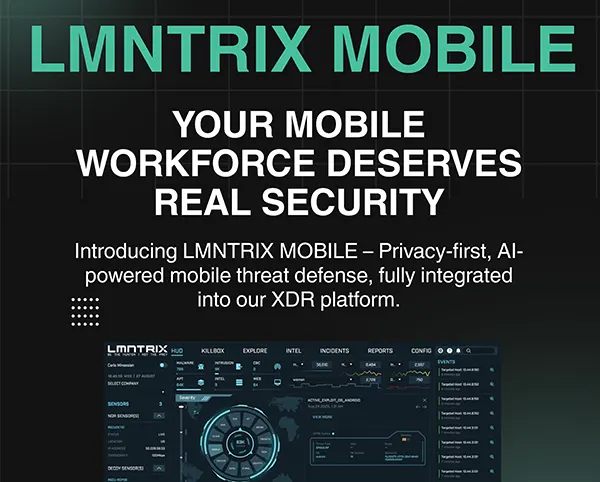
LMNTRIX Mobile Security
Enterprise-Grade Mobile Threat Defense, Built into XDR
Extend real-time protection to iOS, Android, and ChromeOS devices. Detect phishing, malicious apps, rogue networks, device compromise, and zero-day threats without sacrificing user privacy.
Protect the Endpoint Your Security Stack Overlooks
Secure corporate-owned and BYOD devices with on-device machine learning, policy enforcement, and analyst-led response.
Device Security & Compliance
- Detect jailbreaks, rooted devices, outdated firmware, and OS vulnerabilities.
- Assess encryption, lock-screen, and device security posture.
- Quarantine or restrict devices that fall out of policy.
Key Benefits
Secure Every Device,
Connection and Interaction
Protect mobile users across the attack paths that traditional endpoint controls were not designed to see.


- 01Compromised DevicesDetect jailbreaks, rooted devices, vulnerable operating systems, and unsafe configurations.
- 02Rogue NetworksIdentify malicious Wi-Fi, MITM activity, DNS hijacking, and SSL stripping.
- 03Malicious ApplicationsFind malware, spyware, risky sideloaded apps, and excessive permissions.
- 04Mobile PhishingBlock malicious links in SMS, apps, email, and browsers, including previously unseen URLs.
- 05Compliance DriftEnforce encryption, lock-screen, OS-version, inactivity, and application policies.
- 06Managed ResponseGive analysts the context and actions needed to validate, contain, and guide remediation.
- 01. Compromised Devices — Detect jailbreaks, rooted devices, vulnerable operating systems, and unsafe configurations.
- 02. Rogue Networks — Identify malicious Wi-Fi, MITM activity, DNS hijacking, and SSL stripping.
- 03. Malicious Applications — Find malware, spyware, risky sideloaded apps, and excessive permissions.
- 04. Mobile Phishing — Block malicious links in SMS, apps, email, and browsers, including previously unseen URLs.
- 05. Compliance Drift — Enforce encryption, lock-screen, OS-version, inactivity, and application policies.
- 06. Managed Response — Give analysts the context and actions needed to validate, contain, and guide remediation.
Visibility Where Modern Work Happens
Mobile devices are a major attack surface. LMNTRIX combines broad threat coverage with continuous analyst support.
Organizations Affected by Mobile Phishing
Content Categories Continuously Vetted
Analyst-Led Investigation
-
Enroll
-
Assess
-
Detect
-
Correlate
-
Respond
Questions.
Clear answers.
Clear answers about mobile threat defense, privacy, deployment, and policy enforcement.
LMNTRIX Mobile is a privacy-first Mobile Threat Defense module of LMNTRIX XDR for corporate-owned and personally enabled devices.
The service covers iOS, Android, and ChromeOS devices across corporate-owned and BYOD programs.
It detects device compromise, malicious or risky applications, phishing, rogue networks, man-in-the-middle attacks, and policy violations.
Yes. The machine-learning engine runs on the device and can detect known and previously unseen threats without relying on cloud connectivity or signature feeds.
Managed devices can be enrolled through MDM or EMM platforms for zero-touch provisioning. Unmanaged users can enroll by installing the app and scanning a provided QR code.
The privacy-first engine is designed to protect the device without collecting personal content, while administrators can define policies for the categories of device information available to the service.