ARTEMIS
Agentic investigation engine
Correlates across all 14 modules and builds the incident timeline.
- Telemetry pulled
- Attacker path rebuilt
- Blast radius scored
- Containment drafted
- Analyst approves
We deploy independent detection behind the stack you already own, assume it's been bypassed, and contain what gets through in under 30 minutes.
No cost. No commitment. Real detections in your environment within days.

¹ Response times are LMNTRIX MDR service targets measured across confirmed incidents. See the MDR service description.
400+ customers in 85+ countries. Rated by the analysts who define MDR.
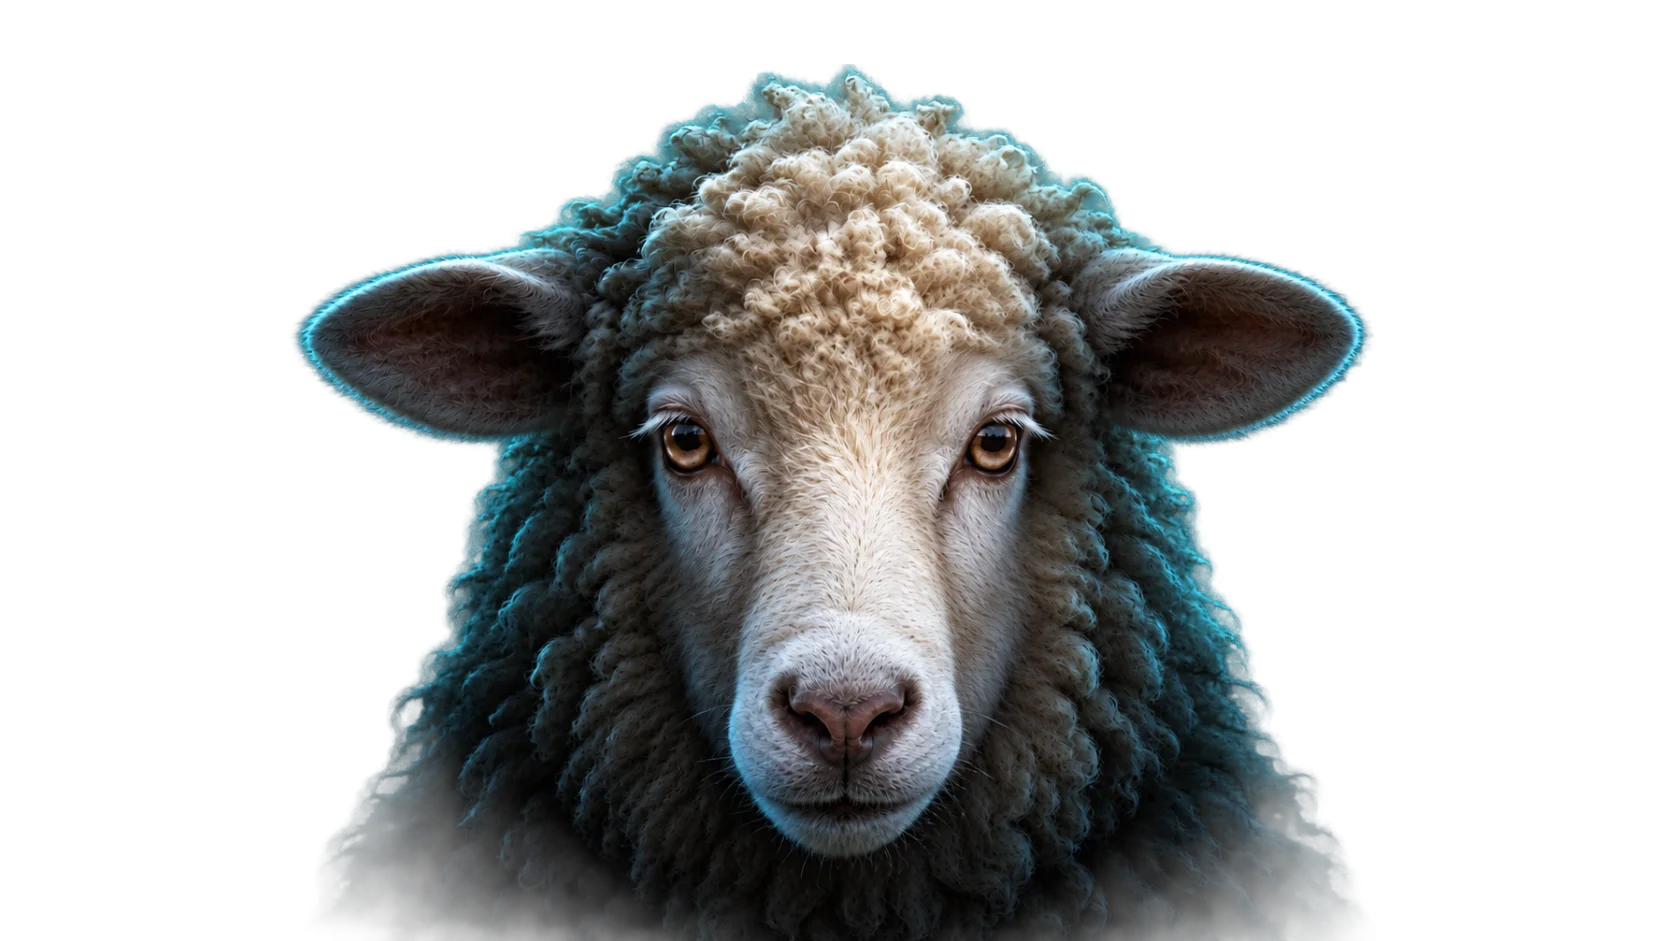
A sheep — the organisation that trusts its tools / A wolf — the hunter that finds the attacker
THE PROBLEM
YOUR STACK TODAY
Firewalls, EDR, and SIEM create walls. Attackers walk around them, then disappear into alert noise.
Intrusions go unnoticed for weeks.
WITH LMNTRIX
5 minutes. No sales call.
BEYOND TRADITIONAL SIEM
Traditional SIEM floods teams with alerts, hides real threats in noise, and drives up cost. LMNTRIX turns fragmented signals into clear, actionable defense.
Stop chasing the same low-value alerts.
Surface real attacks, not endless logs.
Consolidate operations without sacrificing coverage.
We run the full cycle for you — against measured targets, not best efforts.
Detect < 1 min
Investigate < 5 min
Contain & remediate < 30 min
Sensors live within hours, behind your existing tools.
Cross-domain signals and deception expose what your stack misses.
Artemis AI builds the timeline. Analysts confirm it.
Contained in under 30 minutes. No reimaging, no tickets.
Root cause and a board-ready report. Then we close the gap.
Not a managed SIEM. A Cyber Defense Center that acts for you, 24/7.
One platform natively unifying endpoint, network, cloud, identity, mobile, and OT telemetry — with deceptions everywhere and automated response from a single console.
Explore the platform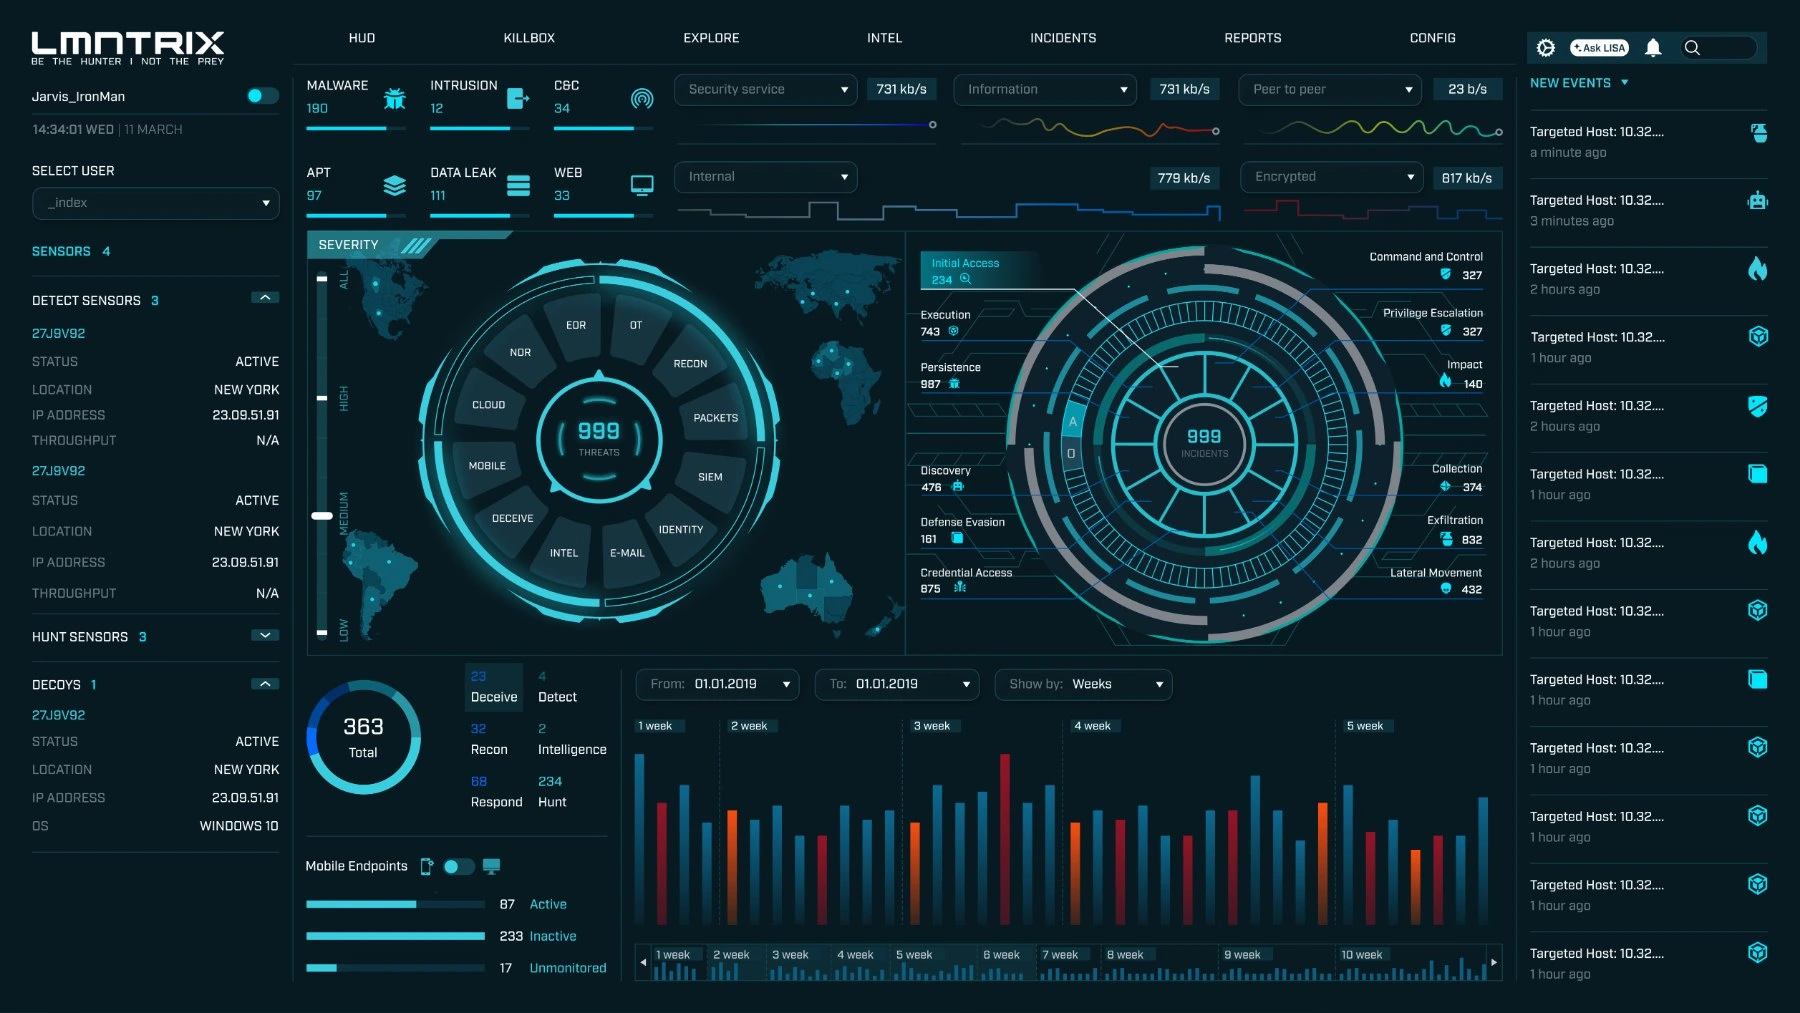


One platform across endpoint, network, cloud, identity, mobile, and OT.
Cross-domain signals correlated to expose what your stack misses.
Contain and shut down attacks — endpoint to cloud, one console.
Trace root cause, close the gap, prevent the repeat.
Every module feeds the same XDR — one data model, one console. Start with what you need, add the rest when you're ready.
LMNTRIX MDR is not an alert-forwarding service. It is seven layers of specialist expertise, operating your detection stack from our Cyber Defense Centers, 24/7/365, with outcomes we are measured on.
Triage every signal, 24/7. Nothing reaches you unvalidated.
Investigate confirmed detections and build the incident timeline.
Contain and remediate on your behalf, surgically, in under 30 minutes.
Reverse the payload, recover the evidence, establish root cause.
Run the Hunt Cycle — Survey, Secure, Detect, Respond — across your environment continuously.
Map global threat activity to your industry, geography, and attack surface.
Keep every sensor tuned, every integration live, every dashboard current.
The capabilities of a modern SOC without the cost of building one — and without the three-year hiring plan.
Every minute of every day, from Cyber Defense Centers in seven countries.
Contained and remediated in under 30 minutes. No reimaging, no downtime.
Forensics and incident response included. No retainer, no hourly clock.
Hypothesis-driven hunts across your telemetry, not just rule matches.
Every quarter, at no cost: an AD audit, cloud security assessment, automated pen test, or darknet exposure review.
98% fewer alerts reaching your team.¹ Every one that does arrives with the full story.
Artemis works every detection like a senior analyst — in seconds, not shifts. Our analysts validate and act.
Correlates across all 14 modules and builds the incident timeline.
Ask about any incident in plain language — from the console, Slack, or Teams.
What happened on this host last Tuesday?
Suspicious PowerShell activity was contained before lateral movement.
“It's like LMNTRIX is playing chess, while others are just playing checkers.”
“In real time, LMNTRIX analysts were baiting attackers and actively pursuing them in our environment — it was like something out of a movie.”
“To build this ourselves, we'd need 50 different products, and then we'd need to find security analysts capable of managing them all.”
“Their deep understanding of our environment allows my internal team to focus on other essential security initiatives.”
“LMNTRIX was the only one that substantiated its cloud detection capabilities — the sole provider that developed its own detections rather than relying on the cloud provider's.”
LMNTRIX deploys behind the tools you already own, uses their telemetry, and adds its own detection. Your investment keeps working — we catch what it missed.
We integrate with the tools we compete against. The question isn't which wall to buy — it's who's watching behind it.
Compatible with CrowdStrike, Palo Alto Networks, Microsoft, Darktrace, Fortinet, Sophos and Mimecast.
We'll deploy LMNTRIX behind your existing controls, at no cost, for 30 days. If we don't surface something your current stack missed, you've lost nothing but the time it took to read this page. If we do, you'll know exactly what you were paying for before — and what you weren't getting.
Prefer a walkthrough first? Book a demoAlready know what you need?
environment within hours, not a six-week project.
for the whole 30 days, including hunting, response, and reporting.
at the end, whether or not you proceed.
Press Enter to see everything we have on the topic.