- PlatformCore Detection & ResponseEDRAdvanced endpoint detection and response with deep visibility, autonomous containment, and analyst-driven investigationNDRNetwork detection and response powered by full packet capture, session reconstruction, and AI-driven anomaly detection.CloudUnified cloud protection across workloads, identities, and SaaS apps, combining visibility with runtime defense.MobileEndpoint security for iOS and Android, detecting malicious apps, phishing attempts, and device-level exploits.IoT/OTCritical asset visibility and threat detection for industrial and IoT environments—without downtime or blind spots.Human Threat Actor CoverageIntelligenceGlobal threat intelligence aggregated from 300+ sources, mapped to your environment for real-time detection and context.Attack ValidationAutomated adversarial validation to confirm detections, test controls, and prioritize real threats over noise.DeceiveDeception technology that lures attackers into decoy environments, revealing tactics before damage is done.IdentityIdentity threat detection and protection with real-time monitoring of Active Directory, Entra ID, and credentials.Post-Breach Forensics & IRPacketsFull-fidelity network forensics with packet capture, file extraction, and retrospective analysis.SIEMCentralized log management and correlation across all telemetry sources for complete security visibility.ReconContinuous adversarial exposure management—simulating attacker reconnaissance to surface hidden weaknesses.
- MDR
- Why LMNTRIX
- Active Defense
- Use CasesBusiness Use CasesReliable & Thorough CybersecurityElevate Security OperationsCross Product CorrelationTech Use CasesCloud Security SimplifiedOptimizing SIEM Security with Next-Gen Detection ToolsAchieve Excellence in Security OperationsComprehensive MITRE ATT&CK Coverage for All StagesEnvironment Use CasesMDR for AWS Cloud Security – 24/7 Detection & ResponseManaged Detection & Response for Google Cloud SecurityAdvanced Microsoft MDR Security for Threat Defense
- LMNTRIX vs the CompetitionLMNTRIX vs other vendorsvs. CrowdStrikeOverhyped, Overpriced & Always Breachedvs. SentinelOneLimited protection, unable to prevent breachesvs. MicrosoftComplex operations increase TCOvs. Palo Alto NetworksDifficult to implement, operate, & maintainvs. SophosOverpriced and Overcomplicatedvs. Trend MicroLimited to own ecosystem & threat of DevOps interruptionsvs. DarktraceOver-promises with flashy AI marketing but always under-deliversvs. other MDRsSlow MDRs that miss threats and leave you to fix the damage
- Ask LISA
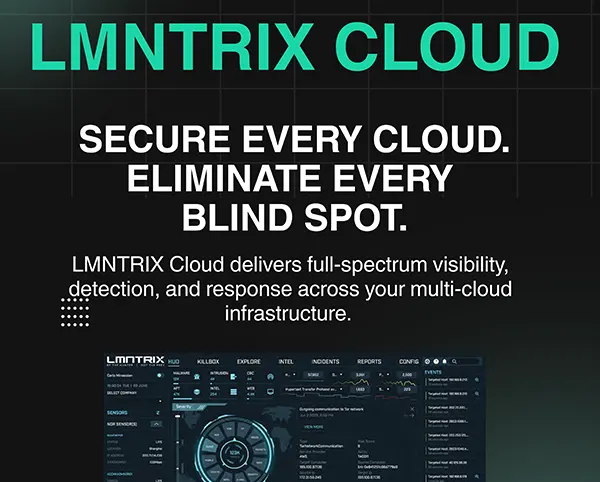
LMNTRIX Cloud
Secure Every Cloud. Eliminate Every Blind Spot.
Unify posture management, runtime detection, identity entitlement analysis, and automated response across AWS, Azure, GCP, and hybrid environments—without invasive agents.
One Platform for Cloud Posture, Identity and Runtime Defense
LMNTRIX Cloud combines CSPM, CDR, and CIEM with real-time telemetry and XDR correlation to expose risk and stop active threats.
Cloud Security Posture Management
- Continuously identify public exposure, weak authentication, and insecure configurations.
- Flag unencrypted data, open ports, and policy violations.
- Prioritize risks and guide or automate remediation.
Key Benefits
Turn Cloud Complexity
into Actionable Security
Protect configurations, identities, workloads, and data while preserving the speed of cloud operations.


- 01Exposure DiscoveryFind public services, open ports, weak authentication, and insecure cloud configurations.
- 02Permission HardeningDetect excessive privileges, unused access, and dangerous entitlement combinations.
- 03Runtime Threat DetectionIdentify credential misuse, privilege escalation, lateral movement, and exfiltration as they occur.
- 04Multi-Cloud VisibilityMonitor accounts, regions, workloads, users, and services from one XDR view.
- 05Continuous ComplianceMeasure cloud posture against recognized standards and produce audit-ready reports.
- 06Automated RemediationApply controlled response logic to risky users, workloads, and configurations.
- 01. Exposure Discovery — Find public services, open ports, weak authentication, and insecure cloud configurations.
- 02. Permission Hardening — Detect excessive privileges, unused access, and dangerous entitlement combinations.
- 03. Runtime Threat Detection — Identify credential misuse, privilege escalation, lateral movement, and exfiltration as they occur.
- 04. Multi-Cloud Visibility — Monitor accounts, regions, workloads, users, and services from one XDR view.
- 05. Continuous Compliance — Measure cloud posture against recognized standards and produce audit-ready reports.
- 06. Automated Remediation — Apply controlled response logic to risky users, workloads, and configurations.
The Misconfigurations and Permissions Attackers Exploit
LMNTRIX Cloud makes common cloud risk factors visible, prioritized, and actionable.
Cloud Incidents Involve Misconfigurations
Breaches Stem from Poor Permission Management
Data Breaches Now Originate in the Cloud
-
Discover
-
Prioritize
-
Detect
-
Remediate
-
Prove
Questions.
Clear answers.
Everything you need to know about cloud posture, runtime threats, permissions, and deployment.
LMNTRIX Cloud is an XDR module that secures public-cloud workloads through CSPM, CDR, and CIEM capabilities across AWS, Azure, and GCP.
Yes. It provides centralized visibility across multiple accounts, regions, and cloud providers and prioritizes corrective action by severity and urgency.
No. The service uses cloud APIs, configuration metadata, and native logs, allowing deployment without agents or dedicated appliances.
Machine learning and behavioral analytics correlate identity activity, permissions, exposed assets, host activity, and network communication into scored attack sequences.
Yes. CIEM compares granted permissions with actual usage, identifies excessive access, and recommends least-privilege changes.
Yes. LMNTRIX Cloud continuously monitors configuration and can generate reports for frameworks including SOC 2, PCI DSS, NIST, CIS, ISO 27001, HIPAA, and GDPR.