
- PlatformCore Detection & ResponseEDRAdvanced endpoint detection and response with deep visibility, autonomous containment, and analyst-driven investigationNDRNetwork detection and response powered by full packet capture, session reconstruction, and AI-driven anomaly detection.CloudUnified cloud protection across workloads, identities, and SaaS apps, combining visibility with runtime defense.MobileEndpoint security for iOS and Android, detecting malicious apps, phishing attempts, and device-level exploits.IoT/OTCritical asset visibility and threat detection for industrial and IoT environments—without downtime or blind spots.Human Threat Actor CoverageIntelligenceGlobal threat intelligence aggregated from 300+ sources, mapped to your environment for real-time detection and context.Attack ValidationAutomated adversarial validation to confirm detections, test controls, and prioritize real threats over noise.DeceiveDeception technology that lures attackers into decoy environments, revealing tactics before damage is done.IdentityIdentity threat detection and protection with real-time monitoring of Active Directory, Entra ID, and credentials.Post-Breach Forensics & IRPacketsFull-fidelity network forensics with packet capture, file extraction, and retrospective analysis.SIEMCentralized log management and correlation across all telemetry sources for complete security visibility.ReconContinuous adversarial exposure management—simulating attacker reconnaissance to surface hidden weaknesses.
- MDR
- Why LMNTRIX
- Active Defense
- Use CasesBusiness Use CasesReliable & Thorough CybersecurityElevate Security OperationsCross Product CorrelationTech Use CasesCloud Security SimplifiedOptimizing SIEM Security with Next-Gen Detection ToolsAchieve Excellence in Security OperationsComprehensive MITRE ATT&CK Coverage for All StagesEnvironment Use CasesMDR for AWS Cloud Security – 24/7 Detection & ResponseManaged Detection & Response for Google Cloud SecurityAdvanced Microsoft MDR Security for Threat Defense
- LMNTRIX vs the CompetitionLMNTRIX vs other vendorsvs. CrowdStrikeOverhyped, Overpriced & Always Breachedvs. SentinelOneLimited protection, unable to prevent breachesvs. MicrosoftComplex operations increase TCOvs. Palo Alto NetworksDifficult to implement, operate, & maintainvs. SophosOverpriced and Overcomplicatedvs. Trend MicroLimited to own ecosystem & threat of DevOps interruptionsvs. DarktraceOver-promises with flashy AI marketing but always under-deliversvs. other MDRsSlow MDRs that miss threats and leave you to fix the damage
- Ask LISA
ONE PLATFORM / ACTIVE DEFENSE
Why LMNTRIX
Fewer Tools. Smarter Defense.
LMNTRIX unifies AI-powered technology, automated response, and 24/7 security expertise in one platform—helping your team detect threats faster, contain them sooner, and operate with less complexity.
Not Another Layer in Your Stack.
Security teams should not have to connect dozens of tools to understand one attack. LMNTRIX brings endpoint, network, cloud, identity, mobile, OT/IoT, and threat intelligence together—so every signal contributes to one clear picture.
-
See the Full Attack
Connect activity across every threat surface.
-
Correlate Every Signal
Turn fragmented telemetry into contextualized incidents.
-
Respond From One Place
Investigate, contain, and remediate without switching tools.
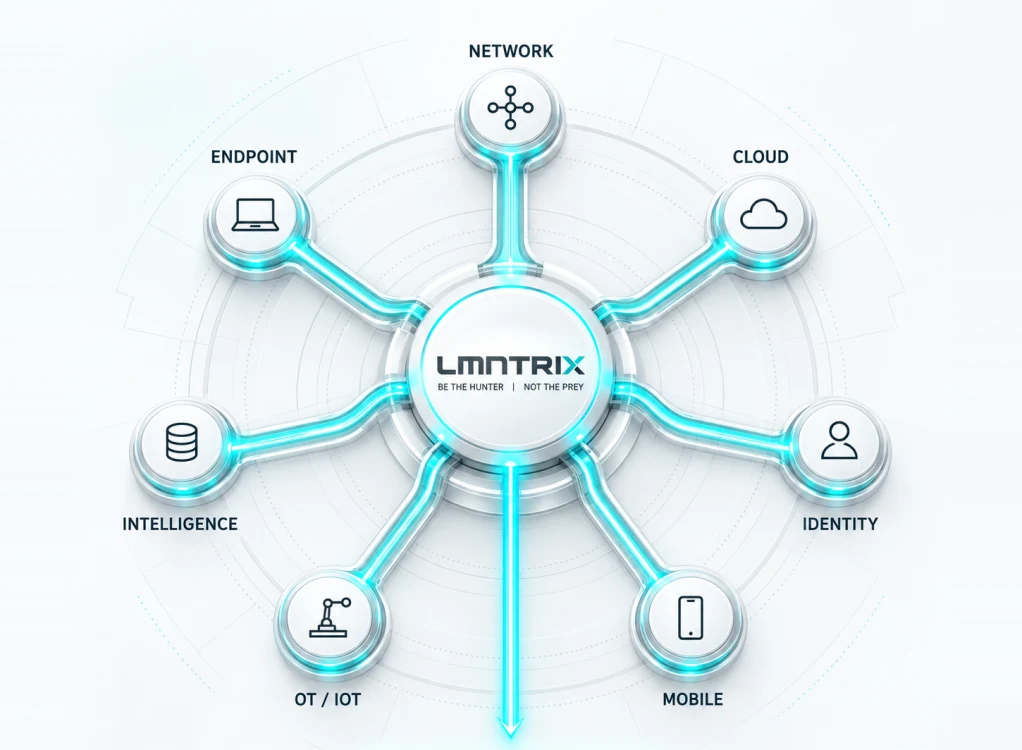
- LMNTRIX
- Network
- Cloud
- Identity
- Mobile
- OT / IoT
- Intelligence
- Endpoint
- Connected Defense
Built to Think. Ready to Act.
Every layer of LMNTRIX works together to detect what others miss, respond at machine speed, and keep expert judgment in every critical decision.
Technology handles scale. Automation delivers speed. Analysts bring judgment.


- 0124/7 SECURITY EXPERTSInvestigate, hunt, and operate as an extension of your team.
- 02AUTOMATED RESPONSEValidates, contains, and remediates threats before they spread.
- 03AI-POWERED DETECTIONFilters noise, identifies anomalies, and reveals hidden attacks.
- 01. 24/7 SECURITY EXPERTS — Investigate, hunt, and operate as an extension of your team.
- 02. AUTOMATED RESPONSE — Validates, contains, and remediates threats before they spread.
- 03. AI-POWERED DETECTION — Filters noise, identifies anomalies, and reveals hidden attacks.
Less Noise. Faster Action. Lower Operational Drag.
Stronger protection without adding operational complexity.
Mean Time to Detect
Mean Time to Respond for 90%+ of incidents
Reduction in False Positives
Automated SecOps & Response
A Security Partner, Not Another Vendor.
We combine continuous protection with clear communication, actionable reporting, and ongoing optimization.
Your team always knows what happened, what we did, and what comes next.
-
01
Understand Your Environment
Align deployment, detection, and response with your priorities.
-
02
Defend Continuously
Monitor, investigate, hunt, contain, and remediate around the clock.
-
03
Improve Over Time
Reporting and continuous tuning strengthen your security posture.
Recognized.
Validated.
Trusted.
Industry recognition and verified compliance—presented clearly.
INDUSTRY RECOGNITION
-
 Recognized
-
 Recognized
-
 Open Source Excellence
-
 Top 250 MSSP
-
 Users’ Choice
VERIFIED COMPLIANCE
-
 Certified
-
 Compliant
-
 Certified
Keep What Works.
Connect What Matters.
LMNTRIX connects the security tools you already use—unifying their telemetry for faster detection, investigation, and response.
Compatible with CrowdStrike, Palo Alto Networks, Microsoft, Darktrace, Fortinet, Sophos and Mimecast.