- PlatformCore Detection & ResponseEDRAdvanced endpoint detection and response with deep visibility, autonomous containment, and analyst-driven investigationNDRNetwork detection and response powered by full packet capture, session reconstruction, and AI-driven anomaly detection.CloudUnified cloud protection across workloads, identities, and SaaS apps, combining visibility with runtime defense.EmailPhishing, BEC, and account-takeover protection deployed behind your native email security, with zero-day sandboxing and content disarm across email and collaboration apps.AI SecurityDiscovery, detection, and response for workforce AI usage and AI agents — shadow AI, sensitive data in prompts, prompt injection, and agent misuse, operated through the same five-verb cycle as every other module.MobileEndpoint security for iOS and Android, detecting malicious apps, phishing attempts, and device-level exploits.IoT/OTCritical asset visibility and threat detection for industrial and IoT environments—without downtime or blind spots.Human Threat Actor CoverageIntelligenceGlobal threat intelligence aggregated from 300+ sources, mapped to your environment for real-time detection and context.ValidateAutomated adversarial validation to confirm detections, test controls, and prioritize real threats over noise.DeceiveDeception technology that lures attackers into decoy environments, revealing tactics before damage is done.IdentityIdentity threat detection and protection with real-time monitoring of Active Directory, Entra ID, and credentials.Post-Breach Forensics & IRPacketsFull-fidelity network forensics with packet capture, file extraction, and retrospective analysis.SIEMCentralized log management and correlation across all telemetry sources for complete security visibility.ReconContinuous adversarial exposure management—simulating attacker reconnaissance to surface hidden weaknesses.
- MDR
- Why LMNTRIX
- Active Defense
- Use CasesBusiness Use CasesReliable & Thorough CybersecurityElevate Security OperationsCross Product CorrelationTech Use CasesCloud Security SimplifiedOptimizing SIEM Security with Next-Gen Detection ToolsAchieve Excellence in Security OperationsComprehensive MITRE ATT&CK Coverage for All StagesEnvironment Use CasesMDR for AWS Cloud Security – 24/7 Detection & ResponseManaged Detection & Response for Google Cloud SecurityAdvanced Microsoft MDR Security for Threat Defense
- Ask LISA
SIEM OPTIMIZATION
Optimizing Your SIEM Security with LMNTRIX
Enhance your SIEM efficiency: cut down on false positives, enrich alerts with essential context, and save on storage expenses.
Overcoming SIEM Challenges
Security Information and Event Management (SIEM) technology is a cornerstone of your security operations. However, effectively using SIEM for threat detection and response presents several challenges.
-
01
Maximizing SIEM Potential
Enhance the value of your SIEM investment by centralizing investigative data and boosting threat detection capabilities with LMNTRIX MXDR.
-
02
Managing SIEM Costs
Although SIEM provides crucial insights, storage costs can impact budgets. Efficient optimization is essential. LMNTRIX XDR for SIEM provides a cost-effective option for long-term data retention and archival.
-
03
Reducing Alert Fatigue
False positives and unclear detection coverage increase workload. SIEMs need ongoing monitoring and custom rules, adding to detection engineering efforts. LMNTRIX MXDR offers near-zero false positives while complementing your existing SIEM investments.
SIEM OPTIMIZATION
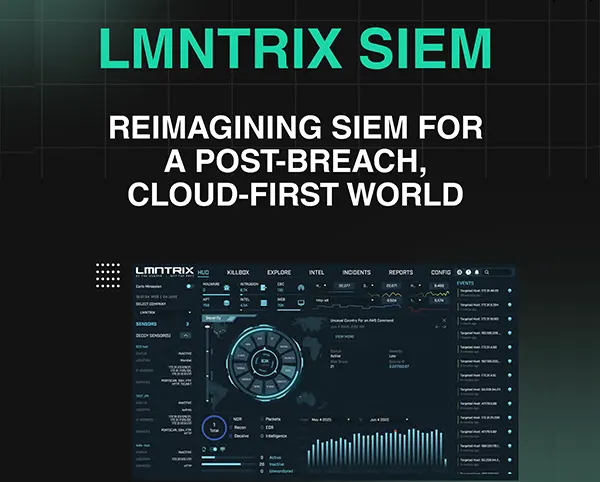
How LMNTRIX Enhances Your SIEM
LMNTRIX provides exceptional decision support for your SIEM, improving alert quality with our unique custom detections to boost incident detection and minimize false positives.
Our services include tuning and contextual enrichment, utilizing LMNTRIX XDR for SIEM for automated investigation, threat hunting, and detection optimization.
We offer insights into effective SIEM detections and actionable recommendations for enhancement.
Additionally, our solution helps reduce storage costs by not requiring all data to be stored in the SIEM, ensuring flexibility as your technology stack evolves.
Customer Testimonials
“Integrating our SIEM with the LMNTRIX XDR platform has provided a more comprehensive view of our security events and alerts across Microsoft 365, Defender, and Azure Active Directory. This integration facilitates quicker and more precise incident responses. The streamlined workflows and reduced manual processes have freed up valuable time, allowing us to address additional security priorities.”
 John Smith
Director of Cybersecurity and Incident Response