- PlatformCore Detection & ResponseEDRAdvanced endpoint detection and response with deep visibility, autonomous containment, and analyst-driven investigationNDRNetwork detection and response powered by full packet capture, session reconstruction, and AI-driven anomaly detection.CloudUnified cloud protection across workloads, identities, and SaaS apps, combining visibility with runtime defense.EmailPhishing, BEC, and account-takeover protection deployed behind your native email security, with zero-day sandboxing and content disarm across email and collaboration apps.AI SecurityDiscovery, detection, and response for workforce AI usage and AI agents — shadow AI, sensitive data in prompts, prompt injection, and agent misuse, operated through the same five-verb cycle as every other module.MobileEndpoint security for iOS and Android, detecting malicious apps, phishing attempts, and device-level exploits.IoT/OTCritical asset visibility and threat detection for industrial and IoT environments—without downtime or blind spots.Human Threat Actor CoverageIntelligenceGlobal threat intelligence aggregated from 300+ sources, mapped to your environment for real-time detection and context.ValidateAutomated adversarial validation to confirm detections, test controls, and prioritize real threats over noise.DeceiveDeception technology that lures attackers into decoy environments, revealing tactics before damage is done.IdentityIdentity threat detection and protection with real-time monitoring of Active Directory, Entra ID, and credentials.Post-Breach Forensics & IRPacketsFull-fidelity network forensics with packet capture, file extraction, and retrospective analysis.SIEMCentralized log management and correlation across all telemetry sources for complete security visibility.ReconContinuous adversarial exposure management—simulating attacker reconnaissance to surface hidden weaknesses.
- MDR
- Why LMNTRIX
- Active Defense
- Use CasesBusiness Use CasesReliable & Thorough CybersecurityElevate Security OperationsCross Product CorrelationTech Use CasesCloud Security SimplifiedOptimizing SIEM Security with Next-Gen Detection ToolsAchieve Excellence in Security OperationsComprehensive MITRE ATT&CK Coverage for All StagesEnvironment Use CasesMDR for AWS Cloud Security – 24/7 Detection & ResponseManaged Detection & Response for Google Cloud SecurityAdvanced Microsoft MDR Security for Threat Defense
- Ask LISA
CLOUD SECURITY
Cloud Protection
Cloud Security Simplified
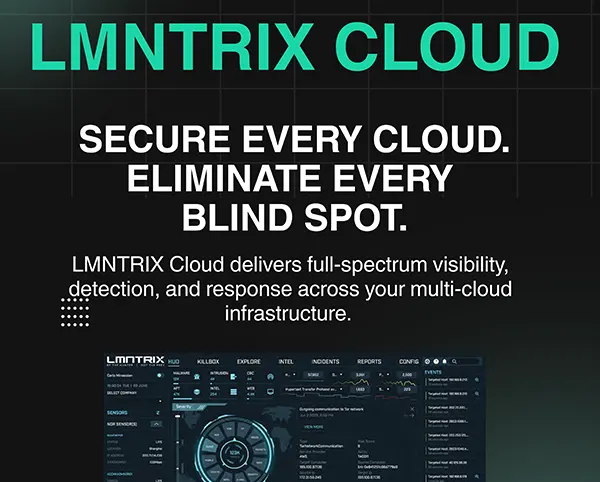
Effortlessly secure your cloud environments with our all-encompassing protection, from CWPP to CNAPP and the Control Plane.
Your Cloud Security Challenges
In 2023, there was a notable 72% rise in cloud infrastructure incidents, as reported by the Expel SOC. This surge in threats demands that your team efficiently manage multiple cloud environments, databases, and policies, requiring both significant time and specialized expertise.
-
01
Cloud Security Gaps
Cloud vendors often provide security tools that generate excessive alerts without sufficient context, making it difficult to prioritize and respond effectively.
-
02
Lack of Holistic Coverage
Current cloud security products and the cloud control plane itself have gaps, and no single vendor offers comprehensive coverage across all diverse cloud workloads.
-
03
Most MDRs Don’t Focus on Cloud
Many Managed Detection and Response (MDR) services do not prioritize cloud security.
CLOUD PROTECTION
How LMNTRIX Can Help
LMNTRIX seamlessly connects with cloud-native application protection platforms (CNAPPs), cloud workload protection platforms (CWPPs), and major cloud services like Amazon Web Services (AWS), Google Cloud Platform (GCP), and Azure. This integration extends to cloud control services and Kubernetes infrastructures, providing comprehensive cloud detection and response.
With real-time monitoring of cloud security products, workloads, and control planes, LMNTRIX offers deep security insights into your cloud environments. This allows for early threat detection and swift response to prevent escalation.
Customer Testimonials
“I appreciate that working with the LMNTRIX team feels collaborative, and they leverage their extensive knowledge of current trends and attack techniques to guide us effectively. With our small team, we lack the resources to constantly research emerging threats—LMNTRIX fills that gap, providing us with vital information that helps us prioritize and refine our security strategy.”
 Shaun Hay
Group Manager Technology and Systems
-

“Our approach to detection is something we take seriously. While many MDR companies can set up a SOC and connect with various technologies to pass on alerts, LMNTRIX stands out by providing the critical context we need. They bridge the gap between us and our tools, delivering insights that truly matter. It's like LMNTRIX is playing chess, while others are just playing checkers.”