


ARTEMIS
Agentic investigation engine
Correlates across all 14 modules and builds the incident timeline.
- Telemetry pulled
- Attacker path rebuilt
- Blast radius scored
- Containment drafted
- Analyst approves
Unified XDR platform with embedded AI analyst (Artemis) and intelligent assistant (LISA). Built to eliminate blind spots, automate response, and accelerate outcomes.
PLATFORM ARCHITECTURE
01
02
03
ARTEMIS
AGENTIC AI ENGINE
04
05
LISA · HUMAN INTERFACE TO THE PLATFORM
HERE’S THE THING.
LMNTRIX XDR isn’t a stitched-together stack of modules. It’s a single, intelligent platform built to ingest everything, think across every threat surface, and act instantly.
Our AI strips away the noise. Our playbooks automate the grind. Our analysts back your team 24/7 — no surprise costs, no red tape.
THE RESULT?
Faster detection. Smarter response. Broader coverage. Lower cost.
That’s what it means to do XDR right.
One platform natively unifying endpoint, network, cloud, identity, mobile, and OT telemetry — with deceptions everywhere and automated response from a single console.
Start a free 30-day POV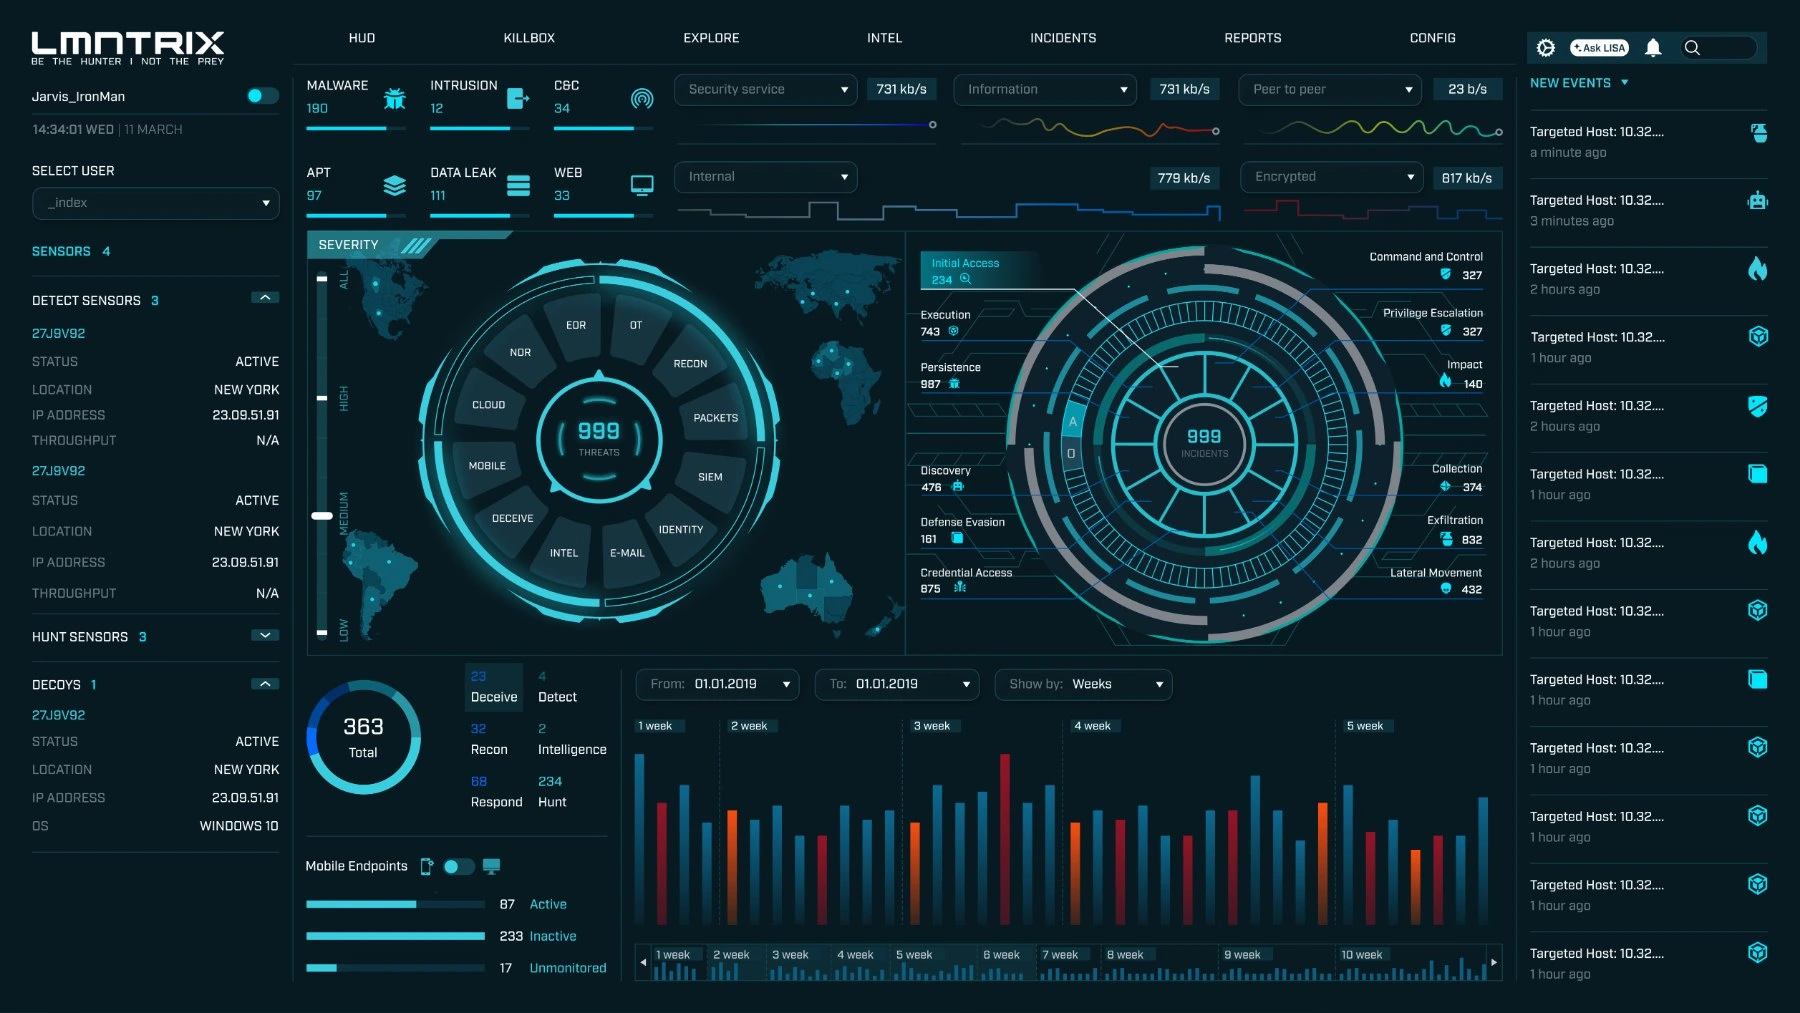


One platform across endpoint, network, cloud, identity, mobile, and OT.
Cross-domain signals correlated to expose what your stack misses.
Contain and shut down attacks — endpoint to cloud, one console.
Trace root cause, close the gap, prevent the repeat.
Every module feeds the same XDR — one data model, one console. Start with what you need, add the rest when you're ready.
LMNTRIX deploys behind the tools you already own, uses their telemetry, and adds its own detection. Your investment keeps working — we catch what it missed.
We integrate with the tools we compete against. The question isn't which wall to buy — it's who's watching behind it.
Compatible with CrowdStrike, Palo Alto Networks, Microsoft, Darktrace, Fortinet, Sophos and Mimecast.
It was built to solve the problems modern security teams actually face: alert fatigue, tool sprawl, slow response, identity blind spots, and threats that slip past traditional detection.
Here’s what we stand for:
Artemis investigates every alert automatically, reasoning in parallel for faster, deeper findings. LISA brings the results to your team inside Slack or Teams — less noise, more clarity, analysts focused on what matters.
One platform built to work together — endpoint, network, cloud, identity, OT, SaaS, mobile, packets and deception, right out of the box. Identity is a primary data source, so lateral movement, abuse and privilege escalation surface faster.
Pre-trained agents resolve most Tier-1 cases without playbooks; containment, rollback and identity isolation move at machine speed, backed by our 24/7 SOC. Fewer tools, fewer false positives, faster outcomes at lower cost.
Competitive comparison
| Capability | LMNTRIX XDR | Palo Alto Cortex | SentinelOne Singularity | CrowdStrike Falcon |
|---|---|---|---|---|
| Agentic AI Investigations | Yes: Artemis + LISA handle Tier 1–2 autonomously | No: Rule-based SOAR | No: Basic LLM integration | Partial: Limited AI triage |
| ChatOps Collaboration | Yes: Native Slack/Teams via LISA | No: No | Partial: Limited in-app | Partial: Falcon assistant UI |
| Human-AI Fusion | Yes: Built-in escalation + feedback loop | No: | No: | No: |
| Unified multi-vector coverage | 14 native modules running hyper-converged | AI-powered modules | Endpoint + network + cloud | Endpoint + cloud + identity |
| Identity-native detection | Identity is core: compromise, lateral, escalation | Partial via acquisition | Ingests identity telemetry | Identity protection module |
| Automation & response | One-click containment, rollback, and DFIR included | Module-based SOAR | Marketplace automations | Agent-driven remediation |
| Network & OT threat detection | Full-packet NDR, deception, and OT integration | Cloud posture + logs | Network visibility via agents | Broad, but limited OT support |
| Human-friendly alerting | Contextual, consensus-based alerts and hunts | AI scoring and alerts | Developer-query tools | Lightweight agent dashboard |
Artemis works every detection like a senior analyst — in seconds, not shifts. Our analysts validate and act.
Correlates across all 14 modules and builds the incident timeline.
Ask about any incident in plain language — from the console, Slack, or Teams.
What happened on this host last Tuesday?
Suspicious PowerShell activity was contained before lateral movement.
We run the full cycle for you — against measured targets, not best efforts.
Detect < 1 min
Investigate < 5 min
Contain & remediate < 30 min
Sensors live within hours, behind your existing tools.
Cross-domain signals and deception expose what your stack misses.
Artemis AI builds the timeline. Analysts confirm it.
Contained in under 30 minutes. No reimaging, no tickets.
Root cause and a board-ready report. Then we close the gap.
Not a managed SIEM. A Cyber Defense Center that acts for you, 24/7.
We'll deploy LMNTRIX behind your existing controls, at no cost, for 30 days. If we don't surface something your current stack missed, you've lost nothing but the time it took to read this page. If we do, you'll know exactly what you were paying for before — and what you weren't getting.
Prefer a walkthrough first? Book a demoAlready know what you need?
environment within hours, not a six-week project.
for the whole 30 days, including hunting, response, and reporting.
at the end, whether or not you proceed.
Press Enter to see everything we have on the topic.