
- PlatformCore Detection & ResponseEDRAdvanced endpoint detection and response with deep visibility, autonomous containment, and analyst-driven investigationNDRNetwork detection and response powered by full packet capture, session reconstruction, and AI-driven anomaly detection.CloudUnified cloud protection across workloads, identities, and SaaS apps, combining visibility with runtime defense.MobileEndpoint security for iOS and Android, detecting malicious apps, phishing attempts, and device-level exploits.IoT/OTCritical asset visibility and threat detection for industrial and IoT environments—without downtime or blind spots.Human Threat Actor CoverageIntelligenceGlobal threat intelligence aggregated from 300+ sources, mapped to your environment for real-time detection and context.Attack ValidationAutomated adversarial validation to confirm detections, test controls, and prioritize real threats over noise.DeceiveDeception technology that lures attackers into decoy environments, revealing tactics before damage is done.IdentityIdentity threat detection and protection with real-time monitoring of Active Directory, Entra ID, and credentials.Post-Breach Forensics & IRPacketsFull-fidelity network forensics with packet capture, file extraction, and retrospective analysis.SIEMCentralized log management and correlation across all telemetry sources for complete security visibility.ReconContinuous adversarial exposure management—simulating attacker reconnaissance to surface hidden weaknesses.
- MDR
- Why LMNTRIX
- Active Defense
- Use CasesBusiness Use CasesReliable & Thorough CybersecurityElevate Security OperationsCross Product CorrelationTech Use CasesCloud Security SimplifiedOptimizing SIEM Security with Next-Gen Detection ToolsAchieve Excellence in Security OperationsComprehensive MITRE ATT&CK Coverage for All StagesEnvironment Use CasesMDR for AWS Cloud Security – 24/7 Detection & ResponseManaged Detection & Response for Google Cloud SecurityAdvanced Microsoft MDR Security for Threat Defense
- LMNTRIX vs the CompetitionLMNTRIX vs other vendorsvs. CrowdStrikeOverhyped, Overpriced & Always Breachedvs. SentinelOneLimited protection, unable to prevent breachesvs. MicrosoftComplex operations increase TCOvs. Palo Alto NetworksDifficult to implement, operate, & maintainvs. SophosOverpriced and Overcomplicatedvs. Trend MicroLimited to own ecosystem & threat of DevOps interruptionsvs. DarktraceOver-promises with flashy AI marketing but always under-deliversvs. other MDRsSlow MDRs that miss threats and leave you to fix the damage
- Ask LISA
AI SYSTEMS SECURITY ASSESSMENT
Secure your AI. Before attackers do.
Deploying large language models (LLMs) is no longer experimental—it’s production. But with innovation comes exposure. Traditional security assessments don’t cut it here. Our AI Systems Security Assessment is built from the ground up to uncover threats unique to LLM pipelines, plugins, prompt handling, and model behavior.
End-to-end, model-specific security.
No distractions. No fluff. This isn’t a generic pentest. It’s a deep dive into how your AI can be exploited—and how to stop it.

Threat Modeling
We start by mapping your LLM ecosystem—APIs, data sources, user flows, and all integration points. Then we identify attack vectors using a simplified STRIDE model tailored for LLMs. Think prompt injection, privilege escalation, jailbreak bypasses, and more.
Configuration & Supply Chain
We evaluate the security posture of your model stack, looking at API keys, RBAC, cloud infrastructure, and third-party dependencies. If your pipeline pulls from GitHub or HuggingFace, we’ll verify it’s not quietly introducing vulnerabilities.
Offensive Testing
We simulate prompt injection and jailbreaks, training data leakage and privacy failures, abuse of tool integrations—including SSRF, command injection, and unauthorized plugin use—and denial-of-service through recursion and complexity overloads.
Logging, Monitoring, & IR
We review your logs, SIEM pipelines, and response plans to make sure they’re actually useful during a live incident. If your LLM gets exploited, will you even know?
Built for Organizations Deploying LLMs
We’ve spent years building XDR platforms to detect, hunt, and respond to adversaries. Now we’re applying that mindset to the new threat surface—AI. Our AI Systems Security Assessment is informed by real-world attacker TTPs, not checkbox audits.
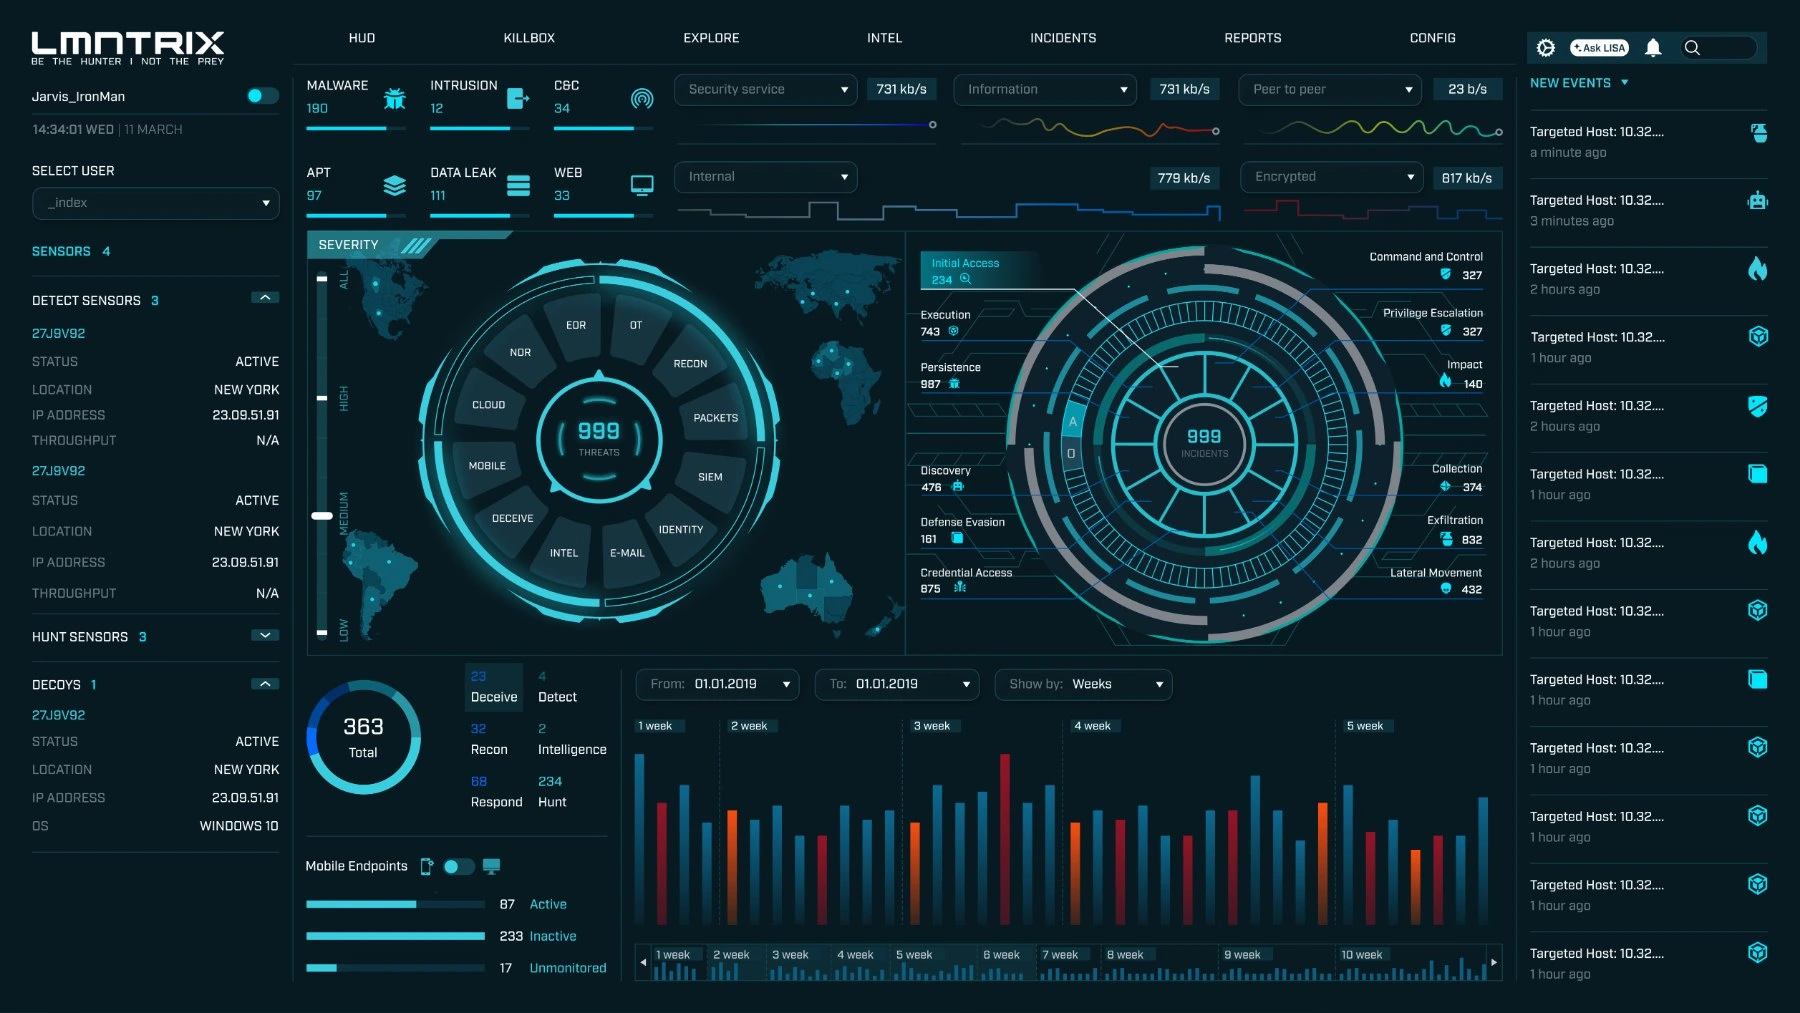


Production LLMs
Enterprises deploying LLMs in production
LLM-Powered Products
Startups integrating LLMs into apps or APIs
High-Stakes AI
Any org that can’t afford to get burned by AI gone rogue
What You Will Get
We don’t dump findings. We deliver clarity.


- 01EXECUTIVE SUMMARYRisks, impact, and recommended actions
- 02TECHNICAL FINDINGSFindings with PoC prompts and attack chains
- 03THREAT MODELThreat model diagrams and risk scoring
- 04REMEDIATION PLAYBOOKRemediation prioritized by impact and exploitability
- 01. EXECUTIVE SUMMARY — Risks, impact, and recommended actions
- 02. TECHNICAL FINDINGS — Findings with PoC prompts and attack chains
- 03. THREAT MODEL — Threat model diagrams and risk scoring
- 04. REMEDIATION PLAYBOOK — Remediation prioritized by impact and exploitability