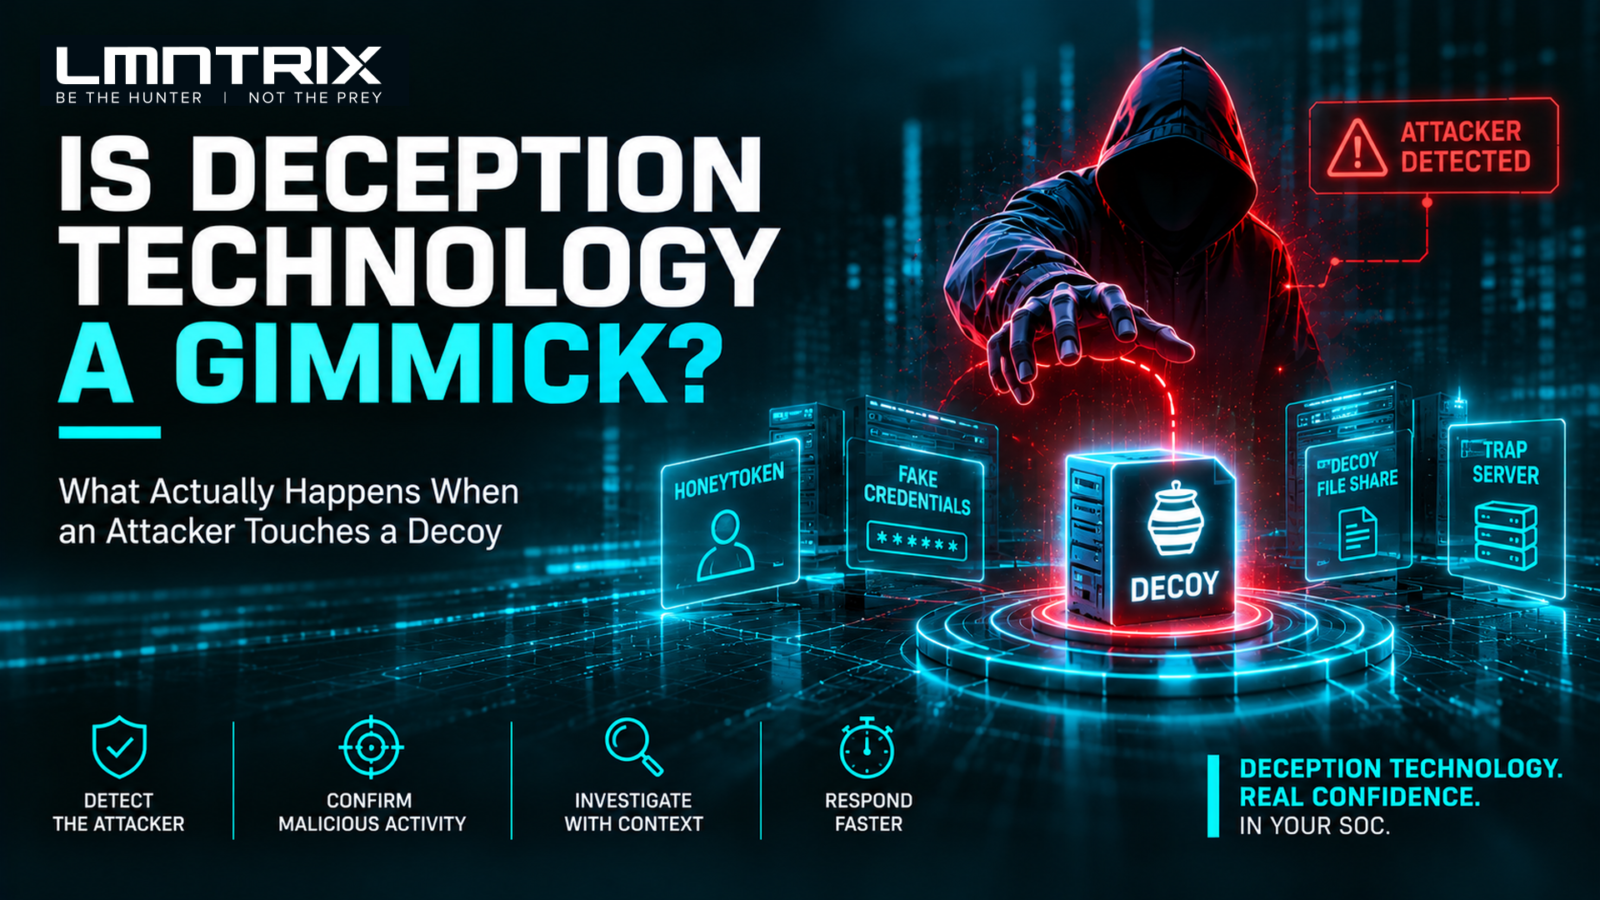
Is Deception Technology a Gimmick? What Actually Happens When an Attacker Touches a Decoy
A fair question deserves a straight answer
Ask a room of security leaders about deception technology and someone will call it a gimmick. Fake servers, fake passwords, a honeypot that a junior engineer set up in 2014 and nobody has looked at since.
It is a fair challenge, and we would rather answer it with evidence than with adjectives. So instead of a feature list, this article walks through what actually happens, minute by minute, when an attacker touches a decoy.
The short answer: deception technology is not a gimmick when it is deployed broadly, kept believable and watched by people who act on every alert. Run as a forgotten honeypot, it is exactly the gimmick sceptics describe.
Deception technology, in one sentence: the practice of planting decoy assets, credentials and data across an environment that no legitimate user has any reason to touch, so that any interaction with them is a high-confidence sign of an attacker.
The case against deception technology, taken seriously
The gimmick reputation was earned. Early deception deployments shared four problems, and buyers who lived through them are right to be wary.
- Isolated honeypots. A single fake server on its own subnet only catches an attacker who happens to scan that subnet. Most never do.
- Decoys that looked fake. Default hostnames, empty file shares and services nobody else in the estate runs. A careful operator spots them and walks around them.
- Set and forget. Decoys that never change stop matching the real network within months. They drift out of the attacker’s path and out of anyone’s attention.
- Alerts with no owner. A decoy alert at 2:00 AM that lands in a queue nobody watches is a log entry, not a detection.
None of these is a flaw in the idea. Each is a flaw in how deception technology was run. That distinction is the whole argument.
What actually happens when an attacker touches a decoy
Here is a realistic intrusion, the kind we see every week. An attacker phishes a finance employee, lands on a laptop and starts working toward the file servers. The endpoint agent sees nothing unusual, because nothing the attacker does yet looks unusual.
09:12: The attacker lands
The attacker opens a session on the laptop with stolen credentials. Nothing fires yet. Planted breadcrumbs sit on the laptop alongside the employee’s real data, waiting to be found.
09:40: The attacker goes looking for credentials
They dump cached credentials and browse for saved RDP sessions. They find a saved session to a “backup” server and a service account with an old password. Both look like a lucky break. Both are planted.
10:05: The attacker maps the network
They query Active Directory for admin accounts and file shares. Decoy accounts and shares appear in the results, indistinguishable from the real ones.
10:31: The attacker takes the bait
They use the planted service account to log in to the “backup” server. The alert fires immediately. No legitimate user has any reason to touch that server or that account, so there is nothing to triage.
10:33: An analyst confirms and investigates
While the attacker lists files on the decoy, an analyst validates the alert. They pull endpoint, identity and network context for the laptop the session came from.
10:50: The attacker is contained
The attacker is still working the decoy, unaware. The laptop is isolated, the session killed and the stolen credentials disabled.
11:30: The path is traced back
The attacker is gone. The team traces the intrusion back to the phishing email and confirms whether any real system was touched.
Times are illustrative; the sequence is not. The attacker was caught during reconnaissance, roughly an hour after landing, before reaching a single real server.
Compare that with the norm. Mandiant’s M-Trends 2026 puts the global median dwell time at 14 days (M-Trends 2026). That is the midpoint across all intrusions, and in practice many attackers stay hidden for hundreds of days. Espionage and North Korean IT worker intrusions had a median dwell time of 122 days, and one campaign Mandiant tracked, BRICKSTORM, went undetected for nearly 400 days.
Deception does not wait for the attacker to do damage. It catches them while they are still looking around.
Why a decoy alert is different from every other alert
Most detection is statistical. A tool scores behaviour against a baseline and raises an alert when something looks unusual. Unusual is not the same as malicious, so most of those alerts are noise.
The numbers show the cost. Vectra’s 2026 research found organisations receive an average of 2,992 security alerts a day, and 63% go unaddressed (Vectra AI). The same summary cites Microsoft and Omdia’s finding that 46% of alerts turn out to be false positives.
A decoy alert works differently. It does not ask whether behaviour is unusual. It asks whether anyone touched something that only an attacker would touch. That gives deception technology three properties no baseline can match:
- Near-zero false positives by design. Real users have no path to a decoy. When one is touched, the question is who, not whether.
- Detection of legitimate-looking activity. An attacker using real tools and valid credentials can look normal to EDR. Using a planted credential cannot look normal, because the credential has no legitimate use.
- Early in the kill chain. Decoys sit where reconnaissance and lateral movement happen, which is before encryption or exfiltration.
MITRE built a framework around this idea. MITRE Engage, which maps deception activities to ATT&CK techniques, frames the shift this way: in traditional defence the attacker only needs to be right once, but with deception the attacker only needs to be wrong once (MITRE).
Where deception technology falls short
Deception is not a silver bullet, and a vendor who says otherwise is selling the gimmick. Be clear about its limits:
- It does not stop initial access. Deception assumes the attacker is already inside. You still need email security, patching, MFA and endpoint protection.
- It only catches what touches it. An attacker who goes straight from one real system to a real target, without exploring, can miss every decoy. Coverage and placement matter.
- It cannot tell you what happened before the touch. A decoy alert tells you an attacker is present. Working out how they got in needs endpoint, identity and network telemetry, ideally with full packet capture to replay the path.
- It decays without care. Decoys must keep matching the real estate as it changes, or they become obvious.
The pattern is clear. Deception technology is a strong detection layer inside a broader programme. It fails when it is treated as the programme.
What makes deception technology work: run it as a managed service
Every shortfall above is an operations problem. That is why we deliver deception technology as part of LMNTRIX Active Defense, our managed detection and response service, rather than as a product your team has to run.
How LMNTRIX delivers it
- Deception everywhere. Decoys, breadcrumbs and honeytoken credentials across endpoints, servers and network segments, in the same platform as our NDR, EDR, identity and full packet capture telemetry.
- Kept believable. Our team maintains decoys so they match your real naming, services and data, and keeps them moving. That is the basis of our moving target defense approach.
- Behind your existing stack. Our sensors sit behind CrowdStrike, Microsoft, Palo Alto or whatever you already own. Anything that reaches a decoy has, by definition, already got past those controls.
- Human-validated. Every alert is validated by an analyst in our Cyber Defense Centers before it reaches you, with a false-positive rate below 0.0001%.
- Contained in under 30 minutes. Containment and remediation are performed by our team, not recommended back to yours.
- Investigated across vectors. A decoy touch starts an investigation across 450+ automated hunts spanning endpoint, network, identity, cloud and packets, so we can show where the attacker came from, not only where they ended up.
Four questions that separate real deception from the gimmick
- Where are decoys deployed: endpoints, servers, network segments, cloud, identity and OT, or one subnet?
- Who keeps decoys believable as the environment changes, and how often do they change?
- What happens in the first 30 minutes after a decoy is touched?
- Is containment performed by the provider, or recommended to my team?
Frequently asked questions
What is deception technology? Deception technology is a cybersecurity approach that plants decoy systems, fake credentials (honeytokens), breadcrumbs and fake data across an environment. Legitimate users never interact with them, so any interaction is a high-confidence signal that an attacker is present.
Is deception technology useful or a gimmick? It is useful when it is deployed broadly, kept realistic and monitored by analysts who act on every alert. It earns the gimmick label when it is a single, unmaintained honeypot with no one watching. The technology is the same; the operating model decides the outcome.
How is deception technology different from a honeypot? A honeypot is one decoy system, usually isolated. Modern deception technology spreads many decoys, credentials and breadcrumbs across endpoints, servers, identity and the network, and lures attackers toward them during reconnaissance.
Does deception technology produce false positives? Very few. Because no legitimate process should touch a decoy, alerts are close to certain. LMNTRIX validates every decoy alert with an analyst, with a false-positive rate below 0.0001%.
Does deception replace EDR or NDR? No. Deception detects attackers who have already got past other controls. It works best alongside EDR, NDR and identity monitoring, which supply the context to investigate and contain what a decoy reveals.
Which MDR providers include deception technology? Few MDR providers deliver deception as a managed capability. LMNTRIX includes deception technology in its Active Defense MDR service, with decoys across endpoints, servers and network segments and containment performed by its own analysts.
A gimmick only if nobody is watching
Deception technology flips the economics of an intrusion. The attacker has to be right about every credential, every share and every server. One wrong guess gives them away, and a team on the other end of that alert can contain them within minutes.
Want to see it in your environment? Our 30-day proof of concept deploys deception and our full Active Defense stack behind your existing controls, with our SOC hunting from day one. Talk to LMNTRIX.